Items tagged with security
Following an eight-year stint as the man in charge of the U.S. National Security Agency (NSA), Army General Keith Alexander has decided to step down effective next March or April. So will his civilian deputy, John "Chris" Inglis, who is planning to retire by the end of the year. The NSA came...
Read more...
This summer, company founder Ladar Levison shut down his secure email service, Lavabit, rather than comply with data requests from the NSA. There is a widespread assumption that Lavabit was the email service used by whistleblower Edward...
Read more...
A hacker (“Craig”) on a site devoted to embedded device hacking posted a lengthy entry detailing how he, on a whim and armed with boredom and too much Shasta cola, reverse-engineered a firmware update and found a backdoor to...
Read more...

In the famous words of a canine scholar best known for his research into unexplainable phenomenon, "Ruh roh!" That about sums up our reaction to the discovery that Google's popular Chrome browser may be storing sensitive data in such a way...
Read more...
The issues of security and privacy should always be on our minds, but ever since the revelation of NSA spying played out this past summer, those issues have been forced to the forefront - impossible to avoid. In reality, that's a great...
Read more...
You can make a fair bit of coin diving into code and rooting out vulnerabilities. In some instances, Microsoft will pay up to $100,000 for a single bug report, and Google's Vulnerability Reward Program routinely pays out thousands of...
Read more...
Are you browsing this very article using a notebook? If so, the trackpad you're probably scrolling with most likely has Synaptics attached in some way. The company responsible for millions upon millions of laptop trackpads has just...
Read more...
Looking for a career change? Consider becoming a professional bug hunter. Don't worry, it's not as gross as it sounds. We're talking about software bugs, such as pieces of code with unintended consequences or underlying security...
Read more...

Payback? Perhaps. With the National Security Agency in the wrong kind of spotlight of late, this is probably sweet for many to read. What's being described as "chronic electrical surges" at an NSA data-storage facility have "hundreds of...
Read more...
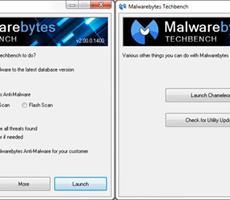
You probably carry with you or have at home a USB thumb drive filled with malware removal tools and other security software. After all, once word gets out that you know a thing or two about computers, the requests from family and friends...
Read more...

In an effort to make online shopping and authentication more secure and less reliant on passwords, an increasing number of companies are joining the FIDO Alliance, which among other things is pushing for the use of fingerprint scanning...
Read more...
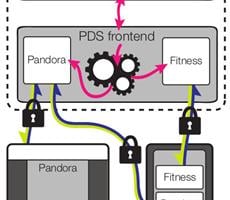
Given the revelations of the NSA’s data-gathering program coupled with the fact that if you use essentially any Internet services your data is out there and capable of being mined, more users than ever are looking for ways to thwart...
Read more...
The average Internet user probably has no idea what "Tor" is. If you're one of those users, you've probably had no good reason to even investigate what it is, what it does, or how it hides. But if you're the NSA, you're acutely aware of Tor, and a new report suggests that both the NSA and GCHQ...
Read more...

Adobe is trying to downplay a recent security breach by saying that "cyber attacks are one of the unfortunate realities of doing business today," and even though that might be true, it's unlikely to provide comfort to the 2.9 million...
Read more...

During an interview at the San Jose McEnery Convention Center this past weekend, antivirus software founder John McAfee touted a new invention that he's planning to launch as soon as possible. It's called D-Central, and based on that name...
Read more...
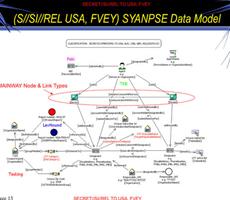
Information about the NSA's data gathering efforts continues, with newly-released information of the agency's efforts on the social networking front. It's already been revealed that the NSA gathers information from many different sources...
Read more...
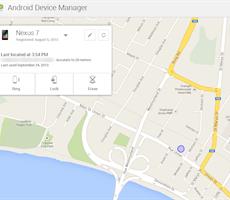
Solutions that enable access to remote devices for security purposes are far from uncommon, but what is uncommon is having the functionality built right into the device, and especially with a solution that's simple to take advantage of. With a recent update to its Android Device Manager...
Read more...
While perhaps a bit unnerving, let's not act like this hasn't happened before. While Apple's engineering team is no doubt massive, there's only so much a fixed group can find. We're talking about bugs in particular; while iOS 7's final...
Read more...
Hot on the heels of news that a crowdfunded competition aims to figure out if the fingerprint security implementation on Apple's iPhone 5s can be exploited comes news of a proven security risk, squarely involving iOS 7. The exploit specifically involves the lockscreen, the most common piece of...
Read more...
When Apple unveiled its iPhone 5C and 5S last week, one of the standout features belonged to the latter: Fingerprint security. In effect, instead of having to type in a quick password to gain access to your phone, the built-in fingerprint...
Read more...
Following the initial leaks against the NSA by Edward Snowden this past summer, there was speculation that what was being exposed would end up hurting the business of US-based tech companies overseas. It's easy to understand why - when...
Read more...
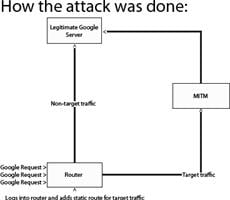
The train carrying a vast amount of NSA confidential information continues to trek along today, with a revelation that the government agency conducted man-in-the-middle (MITM) attacks involving a couple of the Web's largest companies...
Read more...